For MSPs, consultants and assurance teams

Assessment clarity from a local export

Sentry One analyses Palo Alto PAN-OS and Fortinet FortiGate configuration exports on your own machine, applies 19 firewall-focused technical controls, then turns policy, protocol, threat-log and framework evidence into a structured client-ready report.

Assessment runs entirely offline. The optional Remediation module is the only component that contacts a device, and only when you apply an approved change plan.

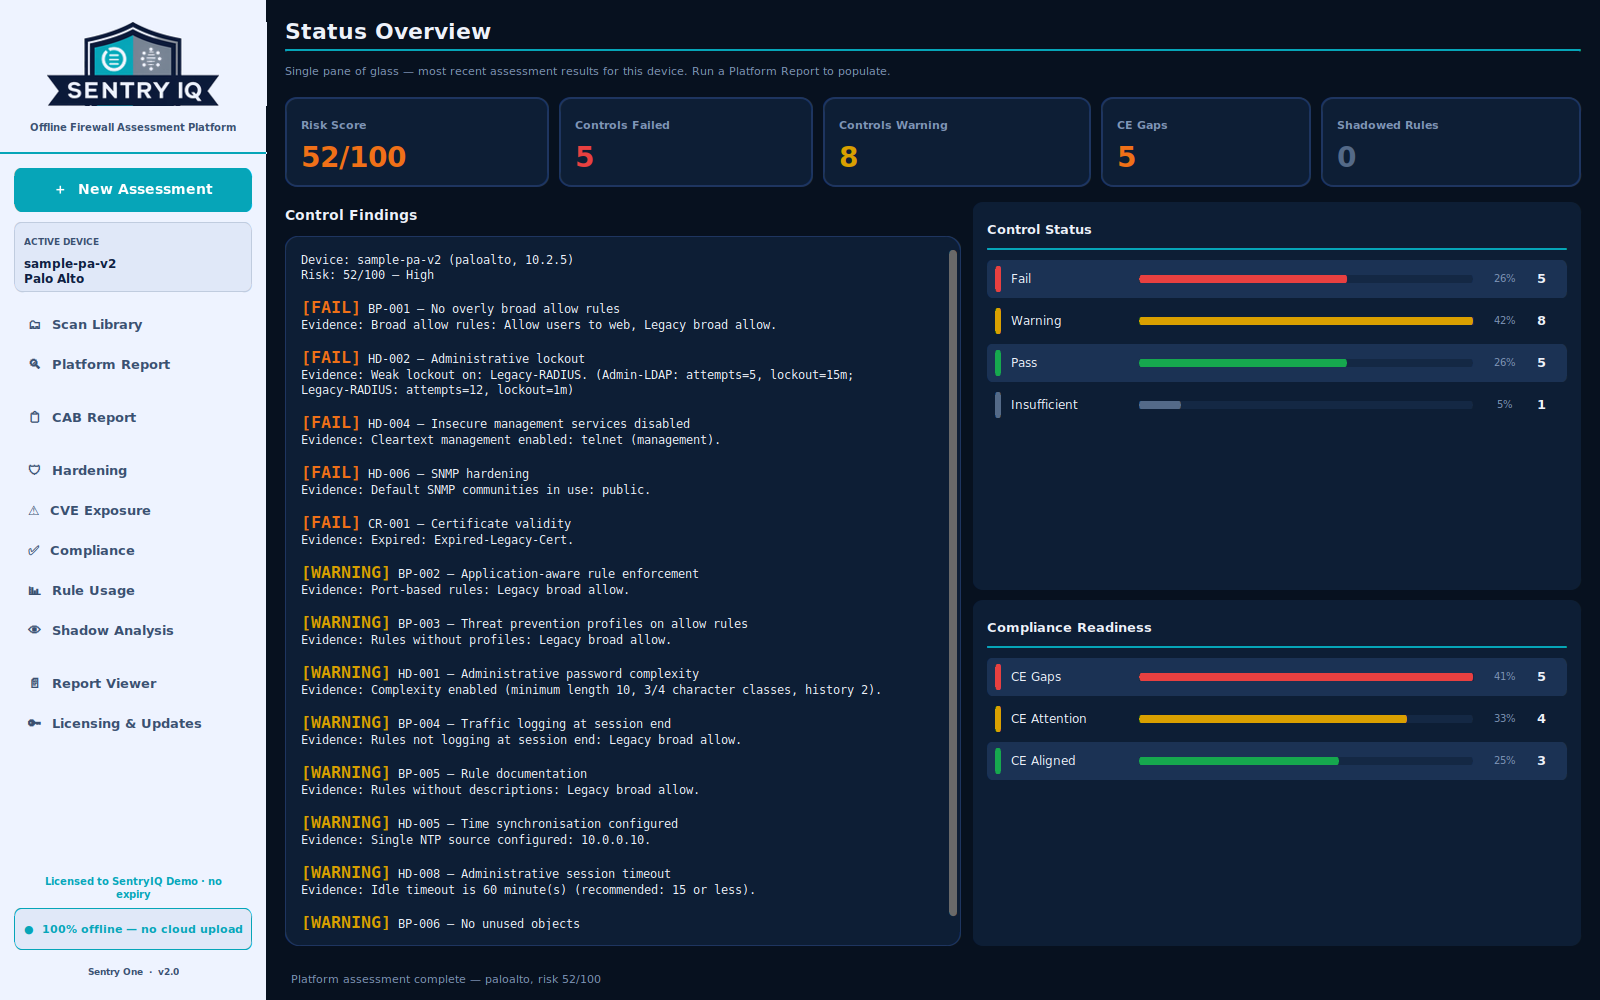
Sentry One status overview showing control findings, risk score and compliance readiness
Status overviewSee the current risk score, control outcomes and compliance readiness for the selected assessment.

Client-ready reporting

See the deliverable before you request a trial

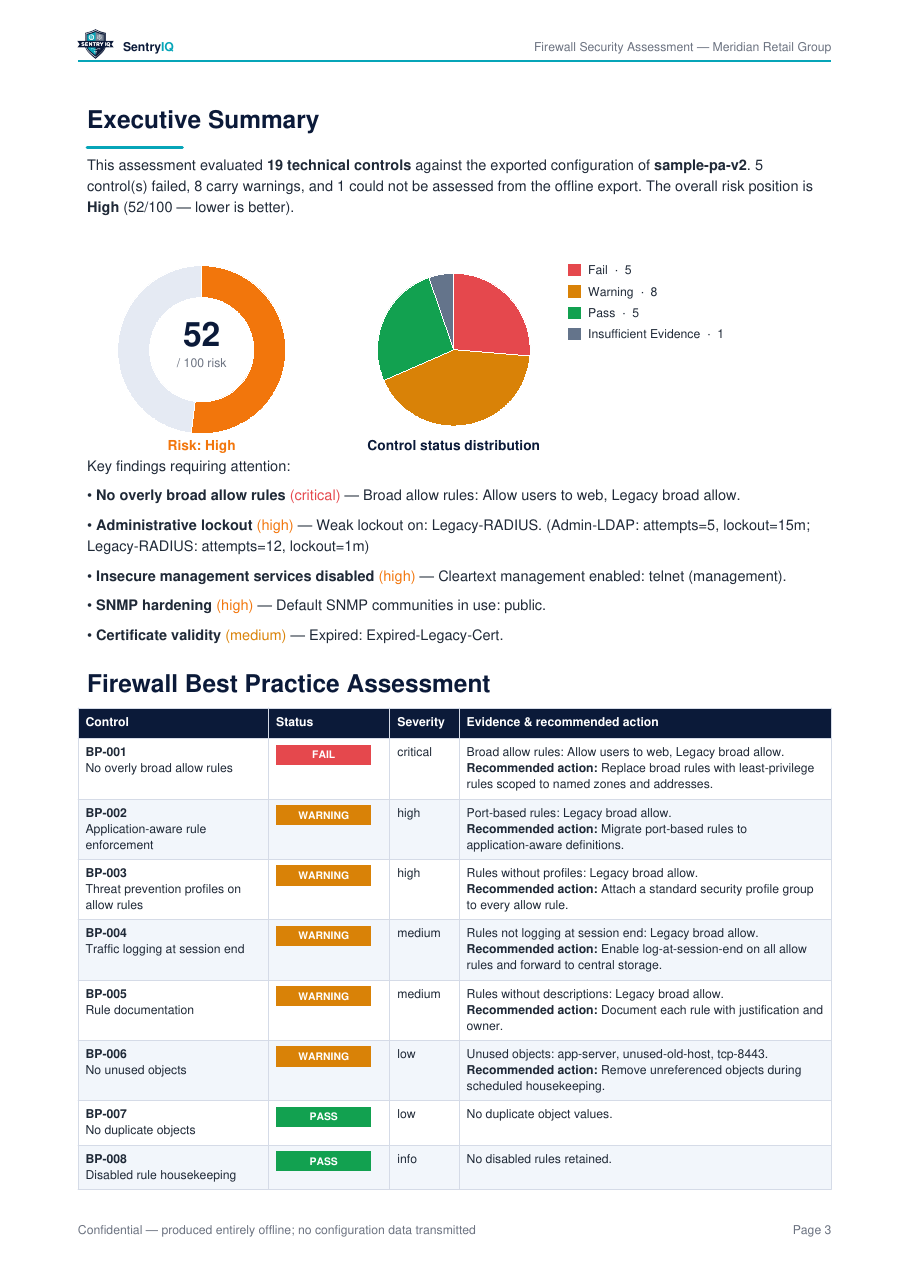
Download a genuine Sentry One report generated from a fictional demo estate. It shows the executive summary, technical findings, CVE context, shadow analysis and framework readiness views without exposing customer data.

  • Direct, ungated PDF download.
  • Clearly watermarked as sample output.
  • Generated by the shipping reporting workflow.
Sentry One sample report executive summary
Executive summaryRisk, control status and prioritised findings in a client-ready format.
19 technical controlsFirewall-focused checks for rule hygiene, protocol exposure, logging, change readiness and assurance context.
PAN-OS and FortiGateStructured assessment support for Palo Alto Networks and Fortinet configuration exports.
No device accessNo credentials, no firewall API access and no cloud upload for the assessment workflow.
Reviewable remediationChange plans are explicit and approved before anything is applied to a device.

Productised workflow

Explicit inputs, controls and outputs

Sentry One is easier to trust when buyers can see the operating model: exported firewall data stays local, analysis is performed against defined controls, and remediation stays reviewable.

Export inLocal analysisFramework mappingReviewable report
assessment.tsevidence.json
assessment:
  source: firewall-export.xml
  mode: offline
  credentials: false
  controls: 19
  frameworks:
    - PCI DSS
    - ISO 27001
    - NCSC CAF

report:
  brandable: true
  remediation: reviewable

Platform capabilities

Built around the assessment workflow

The product is designed for repeatable review: ingest an export, understand the evidence, explain the finding, prepare the report and plan a controlled change.

Platform report

Bring technical evidence into one assessment view

Sentry One combines control findings, evidence, risk context and framework alignment in a single assessment workflow for Palo Alto PAN-OS and Fortinet FortiGate exports.

  • Five honest control states, including insufficient evidence.
  • Technical evidence and remediation attached to each result.
  • One assessment model reused across reports and framework views.
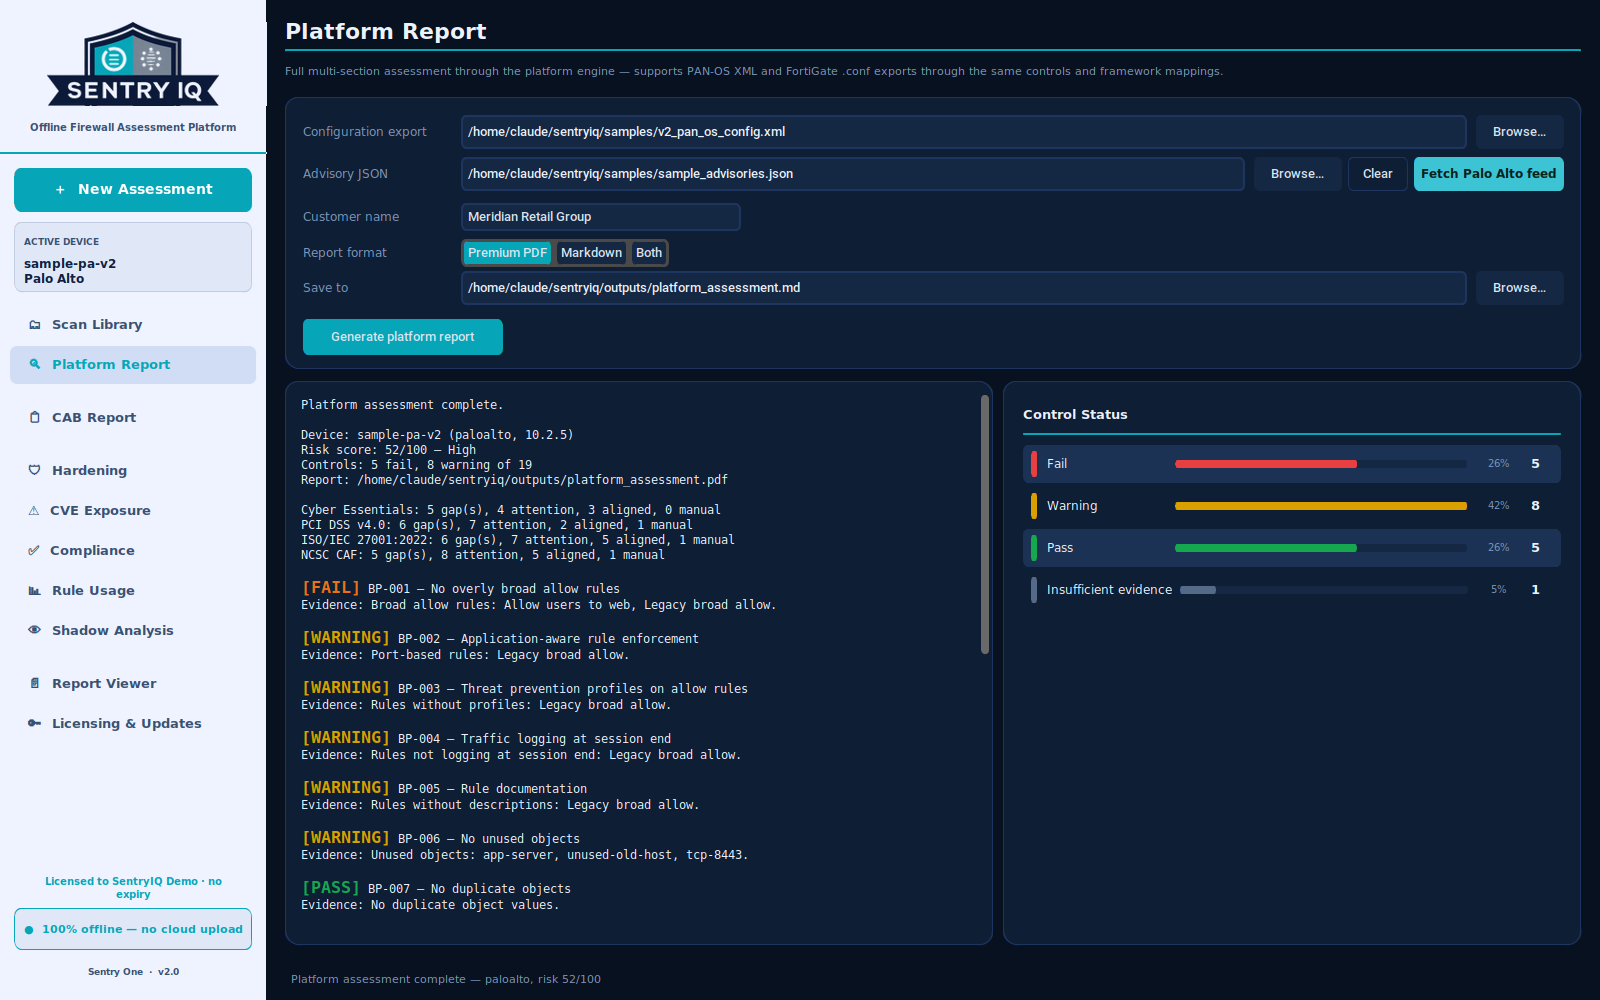
Sentry One Bring technical evidence into one assessment view screen
Platform reportBring technical evidence into one assessment view

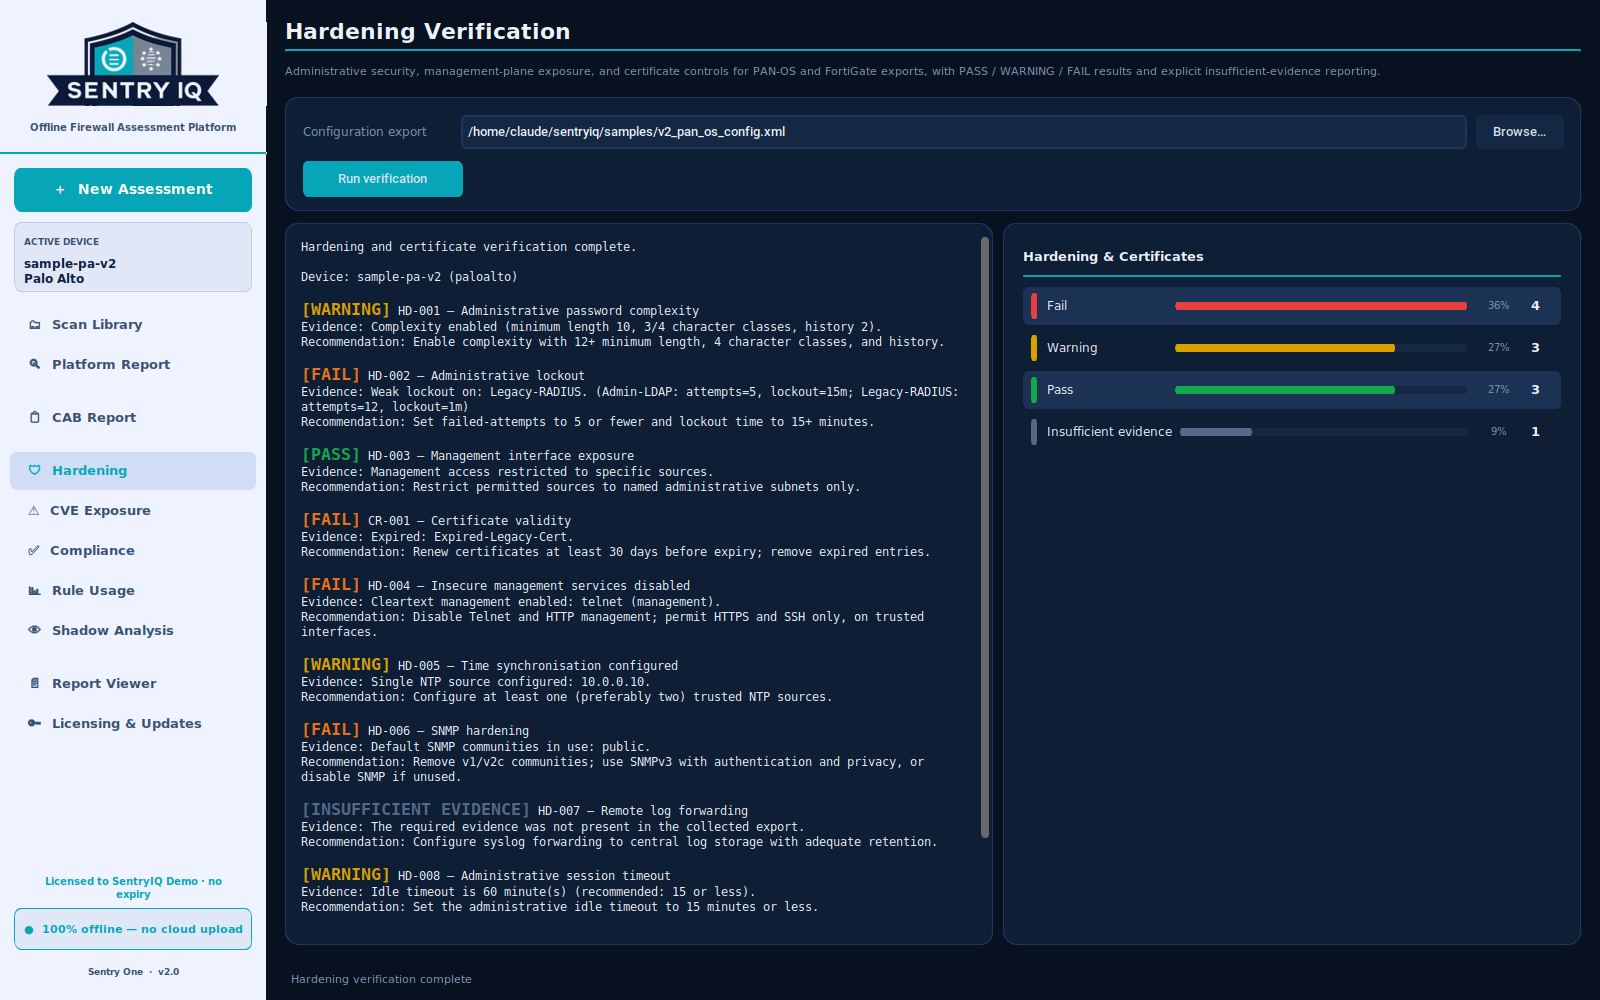
Hardening verification

Check the controls visible in the configuration

Review management access, password and lockout policy, insecure services, SNMP, time synchronisation, remote logging and other configuration-backed hardening signals.

  • Evidence-led pass, warning and fail outcomes.
  • Insufficient evidence is reported rather than guessed.
  • Recommendations remain subject to consultant validation.
Sentry One Check the controls visible in the configuration screen
Hardening verificationCheck the controls visible in the configuration

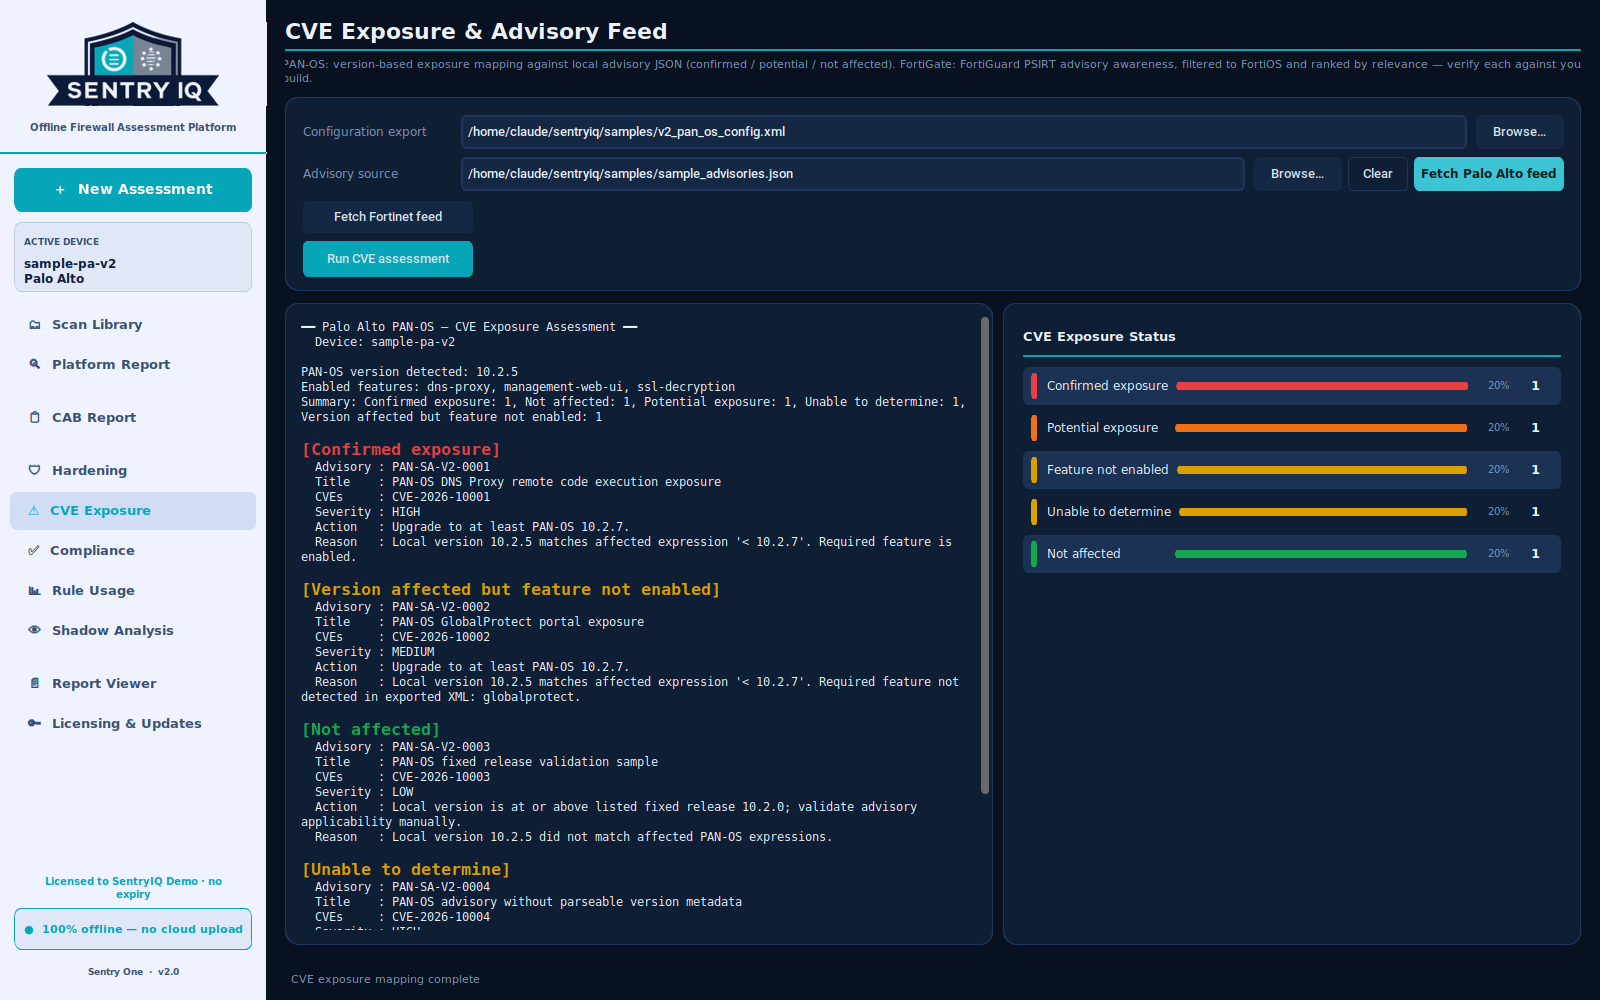
PAN-OS CVE exposure

Relate advisory intelligence to version and features

For PAN-OS assessments, Sentry One compares advisory metadata with the detected software version and enabled features to focus the review on relevant exposure.

  • Feature-aware relevance filtering.
  • Fixed-release guidance where advisory data provides it.
  • Clear confirmed, potential and unable-to-determine states.
Sentry One Relate advisory intelligence to version and features screen
PAN-OS CVE exposureRelate advisory intelligence to version and features

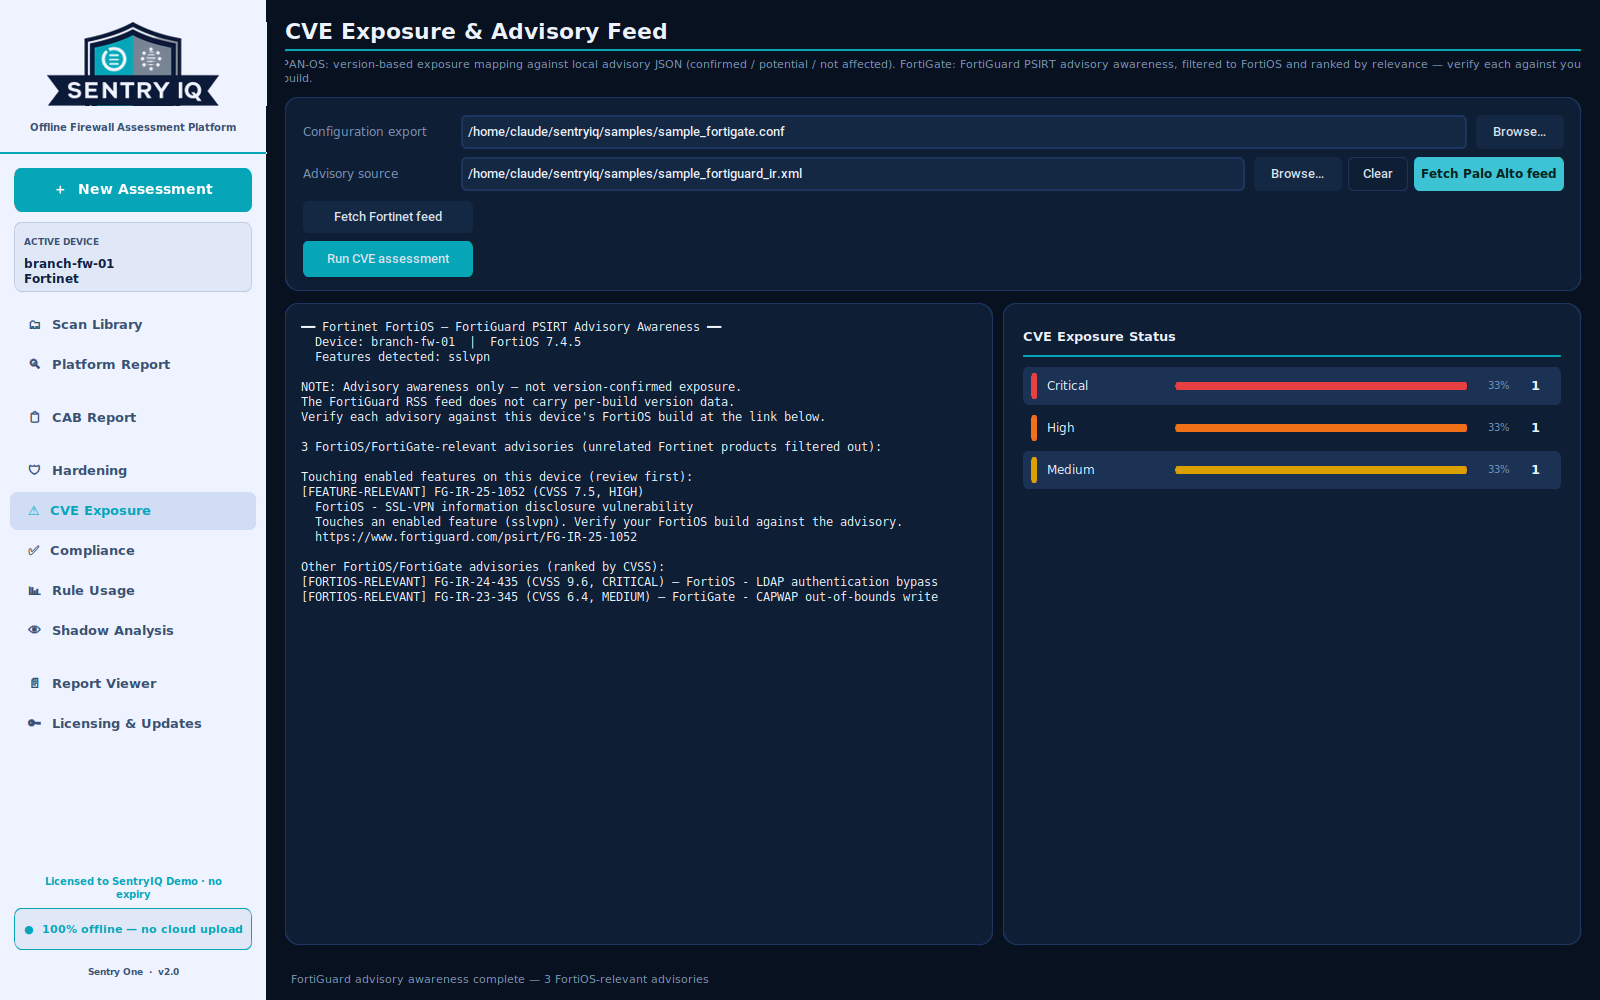
FortiGate advisory awareness

Prioritise relevant FortiOS security advisories

FortiGate assessments surface FortiOS-relevant advisories and rank feature-related items first, while clearly separating awareness from confirmed version exposure.

  • FortiOS and FortiGate advisories filtered from the wider feed.
  • Enabled-feature context, including SSL-VPN relevance.
  • No unsupported claim of confirmed exposure.
Sentry One Prioritise relevant FortiOS security advisories screen
FortiGate advisory awarenessPrioritise relevant FortiOS security advisories

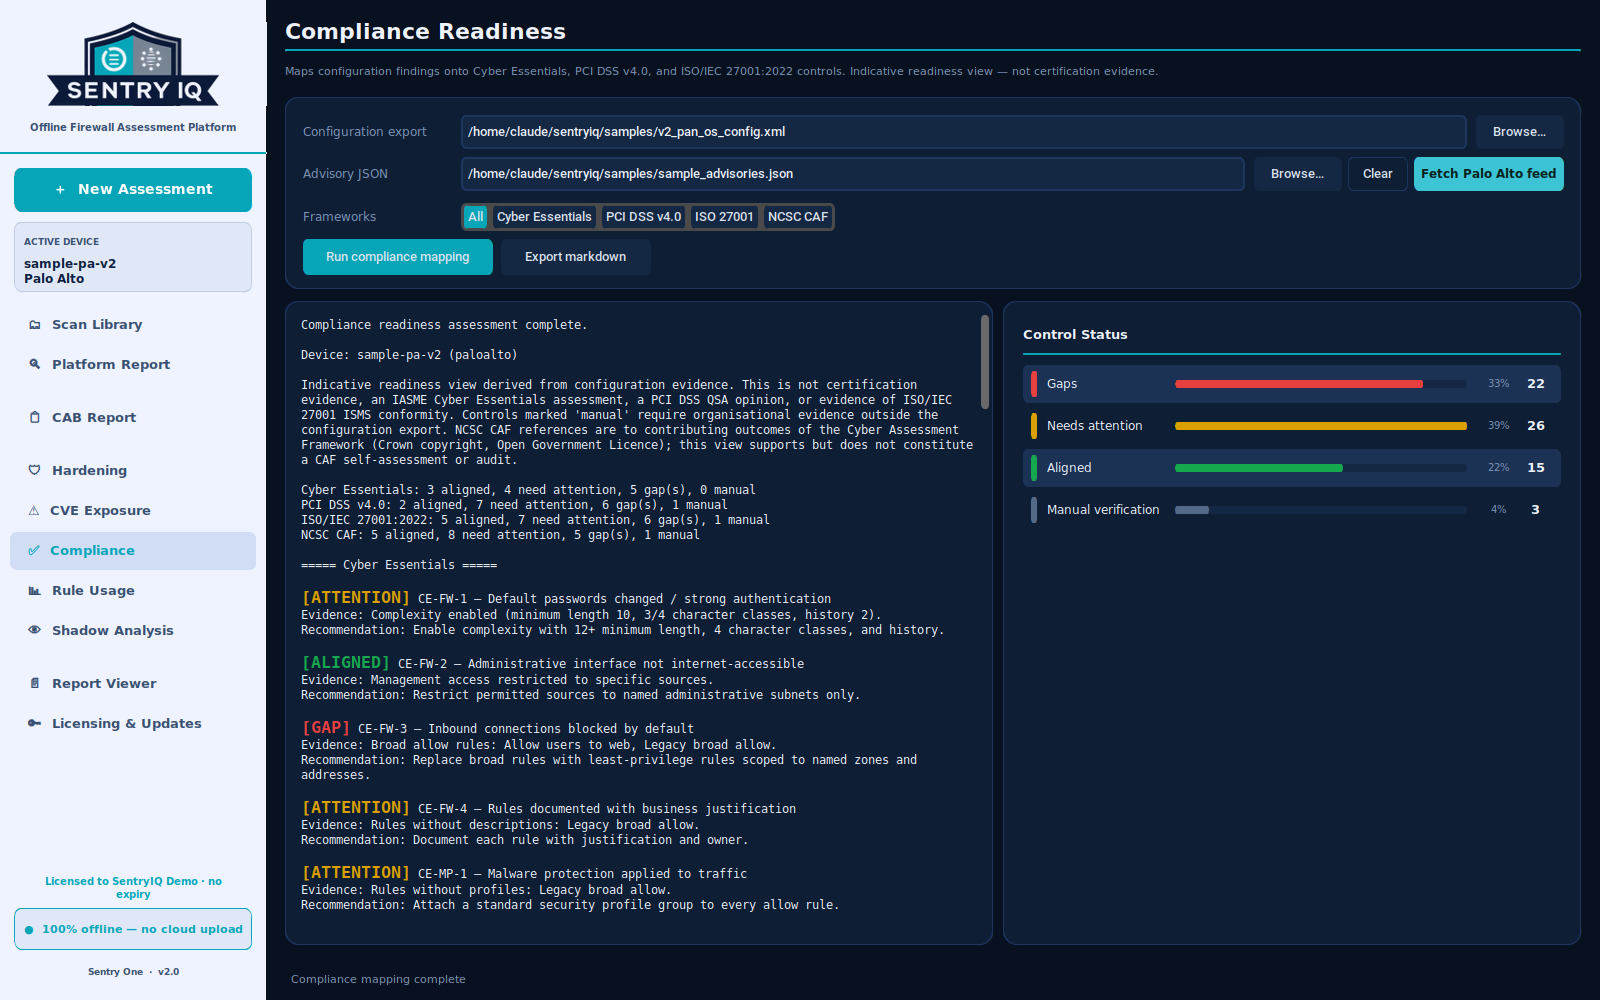
Compliance readiness

Map firewall evidence to recognised frameworks

Cyber Essentials, PCI DSS v4.0, ISO/IEC 27001:2022 and NCSC CAF are presented as indicative readiness views derived from configuration evidence.

  • One configuration export, four assurance views.
  • Clear separation between technical evidence and interpretation.
  • CAF coverage identifies which firewall-evidenced outcomes are in scope.
Sentry One Map firewall evidence to recognised frameworks screen
Compliance readinessMap firewall evidence to recognised frameworks

Shadow analysis

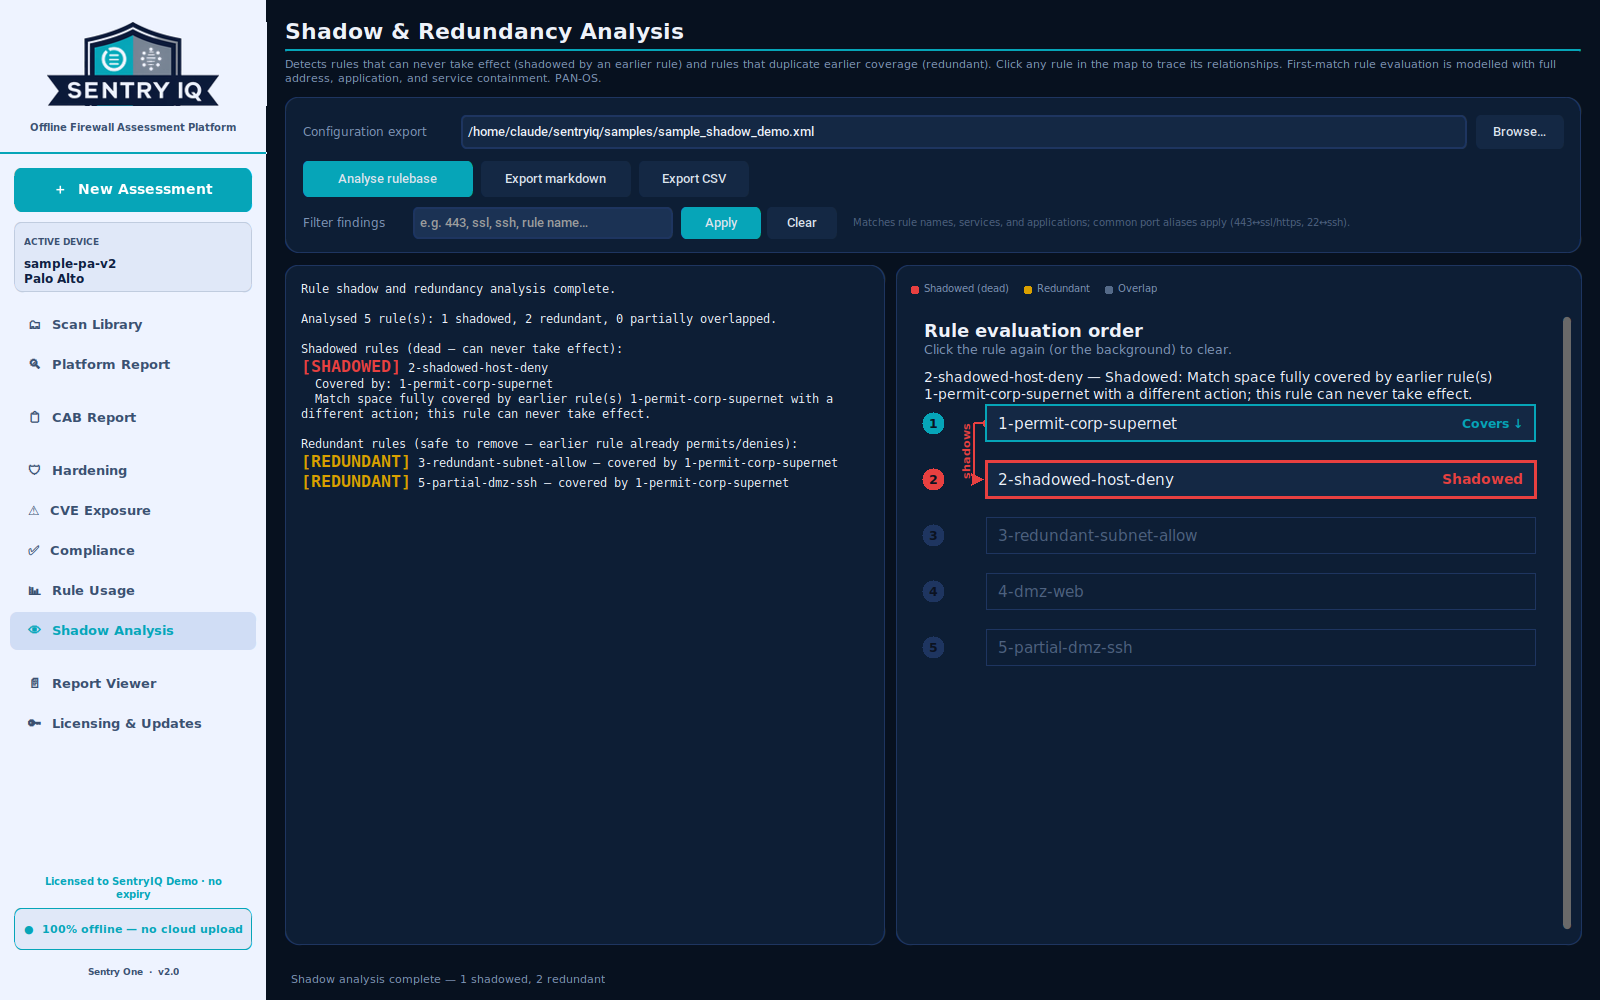
Explain first-match rule behaviour visually

Interactive shadow analysis shows the relationship between affected rules and the earlier policy entries that cover their match space.

  • Filter by rule, application, service or common port alias.
  • Distinguish full shadowing from partial overlap.
  • Export filtered findings for review and change planning.
Sentry One Explain first-match rule behaviour visually screen
Shadow analysisExplain first-match rule behaviour visually

Indicative readiness

One configuration export, four framework views

Sentry One relates firewall findings to Cyber Essentials, PCI DSS v4.0, ISO/IEC 27001:2022 and the NCSC Cyber Assessment Framework as indicative readiness views derived from configuration evidence.

Framework views are indicative readiness mappings based on available firewall configuration evidence. They should be reviewed alongside wider organisational evidence and professional judgement.

Consultancy delivery

Designed to sit behind your service line

The platform supports MSPs, independent security consultants and consultancies delivering repeatable firewall assurance for public-sector and regulated clients.

  • Use the dashboard to show progress across repeat assessments.
  • Use the evidence views to support workshops and remediation calls.
  • Use branded reporting so the deliverable can carry your identity.
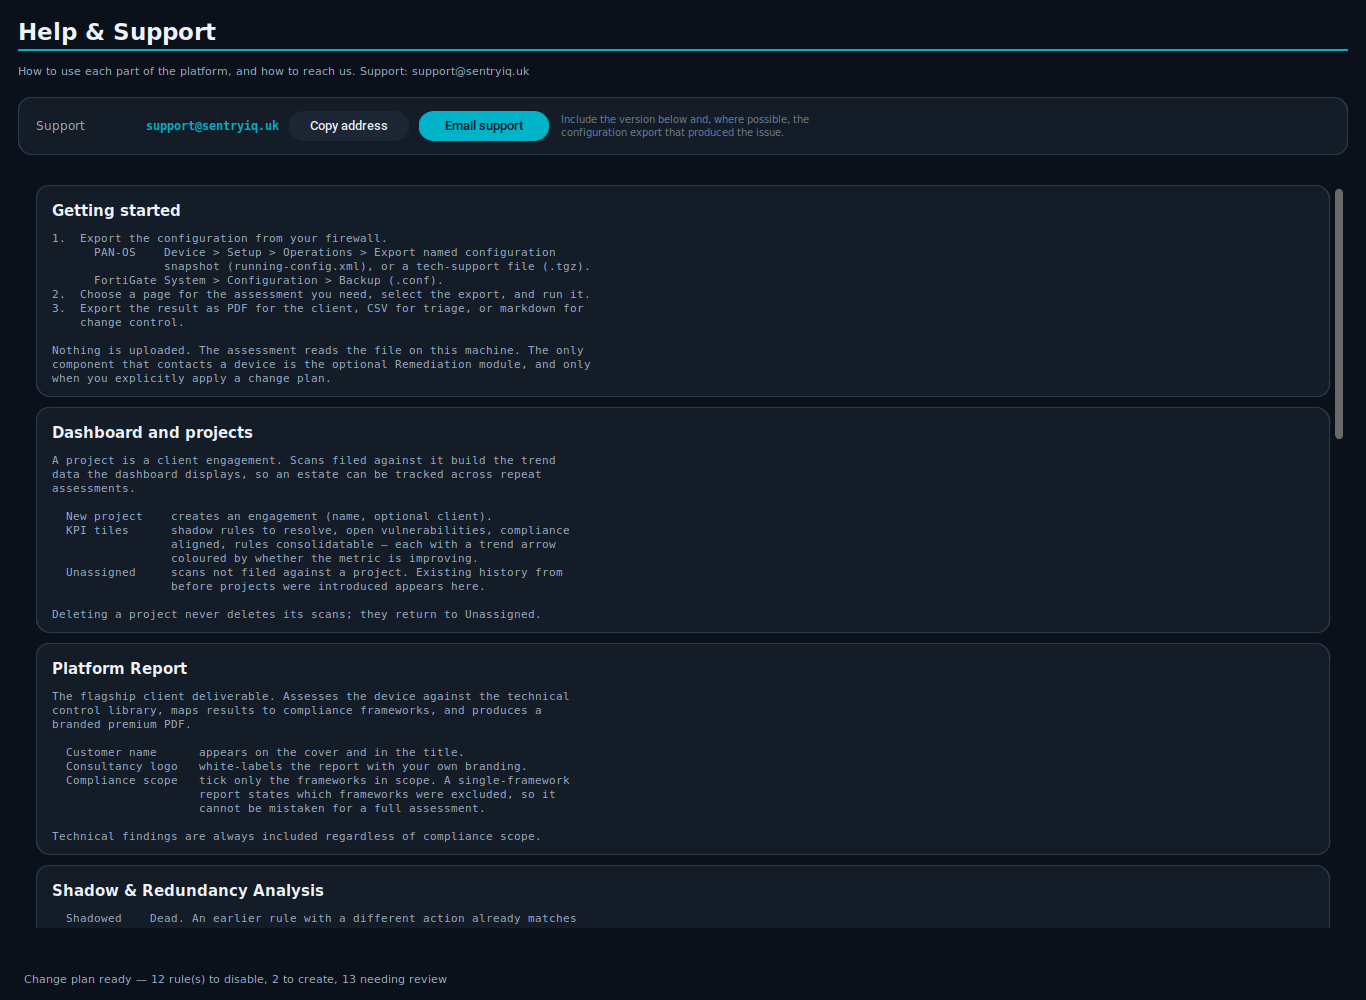
Sentry One help and support screen
Help and supportLaunch support routes and guidance are visible inside the application.

Sentry One

Request a trial

Review the sample deliverable, then email [email protected] to discuss access for your MSP, consultancy or internal assurance workflow.